In this article, we will show how to configure SSH key-based authentication to remotely access Windows workstations and servers. We’ll cover how to generate a public/private key pair on a Windows machine and configure the built-in SSH server in Windows 10/11 and Windows Server 2025/2022/2019 for remote user authentication using via SSH keys instead of account passwords.
SSH key-based authentication is widely used in the Linux world, but in Windows, it has appeared quite recently. The idea is that the client’s public key is added to the SSH server, and when a client tries to connect to it, the server checks whether they have the corresponding private key. This way, a remote user can authenticate in Windows without entering a password.
Generating an SSH Key Pair on a Windows Machine
First, generate a public/private key pair on the client computer, which is the device you’ll use to connect to the remote Windows machine over SSH. The private key is stored on the client-side (keep the key file safe and don’t share it with anyone!). This public key should be added to the authorized_keys file on the SSH server
To generate SSH keys on a Windows client, you must install the OpenSSH Client. On modern Windows versions (starting with Windows 10 build 1709) and Windows Server, the built-in OpenSSH client can be installed as an optional feature using PowerShell.
Add-WindowsCapability -Online -Name OpenSSH.Client~~~~0.0.1.0
Open a non-elevated PowerShell console and use the following command to generate a pair of ED25519 keys:
ssh-keygen -t ed25519
You will be prompted to provide a password to protect the private key (passphrase). If you specify the password, you will have to enter it each time you use this key for SSH authentication. I didn’t enter a passphrase (not recommended).
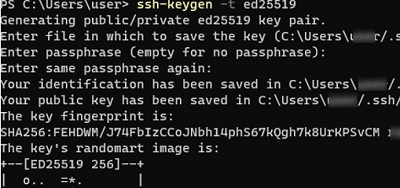
Generating public/private ed25519 key pair.
Enter file in which to save the key (C:\Users\myuser/.ssh/id_ed25519):
Enter passphrase (empty for no passphrase):
Enter same passphrase again:
Your identification has been saved in C:\Users\myuser/.ssh/id_ed25519.
Your public key has been saved in C:\Users\myuser/.ssh/id_ed25519.pub.
The key fingerprint is: SHA256:xxxxxxxx myuser@computername
The key's randomart image is:
+--[ED25519 256]--+
+----[SHA256]-----+
By default, the ssh-keygen command creates the .ssh directory in the current Windows user profile (%USERPROFILE%\.ssh) and saves the generated key pair there.
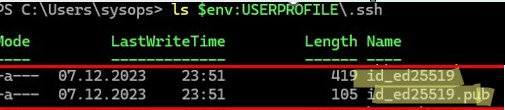 +
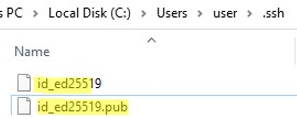
The SSH key pair consists of two files:
id_ed25519– is a private key file which should remain on the client and not be copied anywhere (if you generated an RSA key, the file will be namedid_rsa).id_ed25519.pub– contains the public key. This key will need to be copied to the remote host to which you will connect via SSH (a similar RSA key is calledid_rsa.pub).
Once the SSH keys have been generated, you can add your private key to the SSH Agent service, which allows you to conveniently manage private keys and use them for authentication.
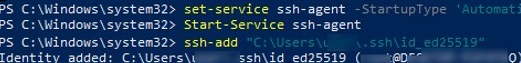
The SSH Agent service stores your private keys and makes them available in the security context of the current user. Run the ssh-agent service and configure it to start automatically using PowerShell:
Set-Service ssh-agent StartupType 'Automatic'
 Start-Service ssh-agent
Add your private key to the ssh-agent:
ssh-add "C:\Users\youruser\.ssh\id_ed25519"
Identity added: C:\Users\youruser\.ssh\id_ed25519 (youruser@computername)
Or as follows:
ssh-add.exe $ENV:UserProfile\.ssh\id_rsa
Configure OpenSSH on Windows for SSH Key-based Authentication
Once you have generated the key pair on the client device, you can proceed with configuring the SSH server. The SSH server in this example is a remote Windows 11 machine that has the OpenSSH service installed and configured.
Check that the OpenSSH server service is installed and running:
Get-WindowsCapability -Online | ? Name -like 'OpenSSH.Ser*'
Get-Service sshd
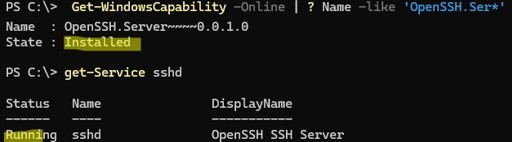
By default, OpenSSH server settings on Windows are stored in the text configuration file C:\ProgramData\ssh\sshd_config. Key-based authentication is not enabled by default in the sshd_config file. You can get a list of allowed authentication methods in OpenSSH by grepping the config file:
cat "C:\ProgramData\ssh\sshd_config"| Select-String "Authentication"
#PubkeyAuthentication yes
#HostbasedAuthentication no
#HostbasedAuthentication
PasswordAuthentication yes
#GSSAPIAuthentication no
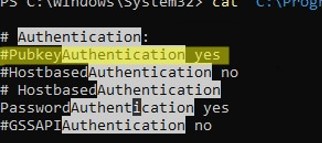
In my example, the PubkeyAuthentication line is commented out, which means that this authentication method is disabled. Open the sshd_config file with Notepad and uncomment the line:
Notepad C:\ProgramData\ssh\sshd_config
PubkeyAuthentication yes
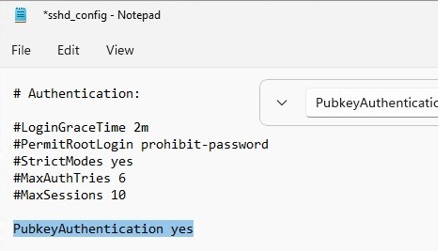
Restart the sshd service after making any changes to the sshd_config file:
Restart-service sshd
Additionally, you can disable password-based SSH auth in the sshd_config file. Configure the following option:
PasswordAuthentication no
Or enable the option using the PS command:
(Get-Content C:\ProgramData\ssh\sshd_config).Replace("#PasswordAuthentication yes","PasswordAuthentication no") | Set-Content C:\ProgramData\ssh\sshd_config
Copy an SSH Public Key to Admin and Non-Admin Users in Windows
Then copy the value from the public key file (id_ed25519.pub) from the client machine to the SSH server. Where to copy the public key value depends on whether the user account you use to connect as is a member of the local Administrators group or not.
- For standard Windows users (non-admins), SSH public keys are added to the authorized_keys file in the user profile. This behaviour is defined by this parameter in the config file:
Get-Content C:\ProgramData\ssh\sshd_config | Select-String -Pattern "^AuthorizedKeysFile"AuthorizedKeysFile .ssh/authorized_keys

- For local administrators, keys must be added to the file C:\ProgramData\ssh\ administrators_authorized_keys . This is also set in the config:
Get-Content C:\ProgramData\ssh\sshd_config -Tail 2 Match Group administratorsAuthorizedKeysFile __PROGRAMDATA__/ssh/administrators_authorized_keys



Let’s assume you want to configure remote SSH access for an unprivileged (non-admin) user named user1.
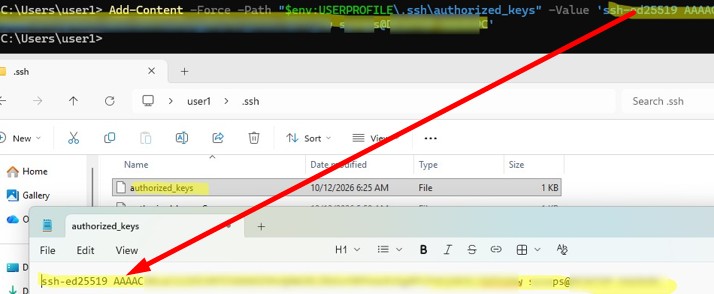
Copy the id_ed25519.pub file to the .ssh directory in the profile of the user under which you will connect to the SSH server. For example, I have a user1 account on a remote Windows 11 machine, so I need to add my public key value to the file C:\Users\user1\.ssh\authorized_keys.
You can add multiple public keys to a single authorized_keys file, with each key on a new line.
If the .ssh directory does not exist in the profile, create it manually.
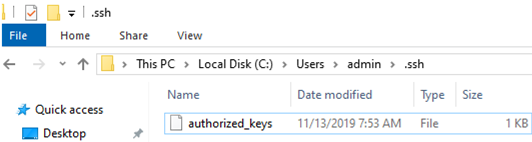
You can copy the public key to the SSH server from the client using the SCP command:
scp C:\Users\youruser\.ssh\id_ed25519.pub admin@192.168.1.15:c:\users\admin\.ssh\authorized_keys
Or copy the contents of the public key file on a client to the clipboard.
Get-Content C:\Users\woshub_adm\.ssh\id_ed25519.pub|Set-Clipboard
Copy the public key value and paste it into the following PowerShell commands, then run them on the SSH server. This will add the new public key value to the user’s profile:
New-Item -ItemType Directory -Force -Path "$env:USERPROFILE\.ssh"
 Add-Content -Force -Path "$env:USERPROFILE\.ssh\authorized_keys" -Value 'ssh-ed25519 AAAAxxxxxxxxxx woshub_adm@myadminPC'
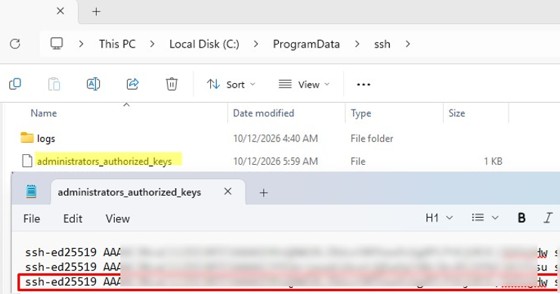
S-1-5-32-544). By default, the SSH public keys of these users are read from a single file, C:\ProgramData\ssh\administrators_authorized_keys, rather than the authorized_keys file in each user profile.To enable SSH connections for these users, add their public keys to this text file. Open the C:\ProgramData\ssh\administrators_authorized_keys file and paste the client’s public SSH-ED25519 key value into it.
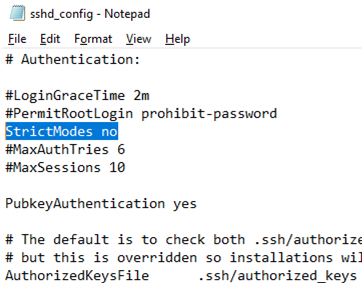
In older versions of OpenSSH, you had to disable StrictModes in the sshd_config configuration file to allow remote connections under admin users. This mode is enabled by default and prevents SSH key-based authentication if the private and public keys are not properly protected. Uncomment the line #StrictModes yes and change it to StrictModes no
For security reasons, access to the sshd_config file should only be granted to the Administrators group and the SYSTEM account. You can change the NTFS permissions on a file with:
You can change the NTFS permissions on a file with:
- The icacls tool:
icacls.exe "C:\ProgramData\ssh\administrators_authorized_keys" /inheritance:r /grant "Administrators:F" /grant "SYSTEM:F" - or using the Get-Acl and Set-Acl PowerShell cmdlets:
Get-Acl "$env:programdata\ssh\ssh_host_rsa_key" | Set-Acl "$env:programdata\ssh\administrators_authorized_keys"

After this, SSH key-based authentication works even when StrictModes option is disabled.
#Match Group administrators
# AuthorizedKeysFile __PROGRAMDATA__/ssh/administrators_authorized_keys
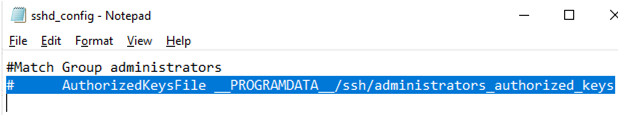
Restart the OpenSSH server:
restart-service sshd
Connect to a Windows SSH Server Using a Private Key from a Windows Client
You can now connect to your Windows computer over SSH without entering a password.
To connect to a remote host using the built-in Windows SSH client, use the following command:
ssh (username)@(SSH server name or IP address)
For example:
ssh user1@192.168.1.15
It means that you want to connect to a remote SSH server with the IP address 192.168.1.15 under the user1 account. The SSH Agent service will automatically attempt to use the previously saved private key for authentication. If you have not set a password (passphrase) to protect the private key, you will be connected to the remote Windows SSH host automatically.
The first time you connect to the host, you need to add the SSH server key fingerprint to the trusted list. Type yes -> Enter.
The authenticity of host '192.168.1.15 (192.168.1.15)' can't be established.
ECDSA key fingerprint is SHA256:xxxxxxx.
Are you sure you want to continue connecting (yes/no/[fingerprint])? yes
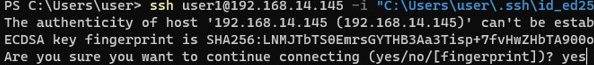
Here are some additional useful SSH client options:
-v– show a detailed SSH connection log-i– manually specify the path to the private key file:ssh user1@192.168.1.15 -i "C:\Users\youuser\.ssh\id_ed25519"- To connect to an SSH host using an Active Directory domain user account, use the following format:
ssh jsmith@woshub.com@192.168.1.15илиssh woshub\jsmith@srv01
ETW logging is used in Windows OpenSSH to store SSH logs instead of plain text files. You can check the SSH key-based authentication logs in the Windows Event Viewer (Application and Services Logs -> OpenSSH -> Operational).
A successful SSH connection with the private key will result in the following event being logged in the OpenSSH log:
EventID 4
sshd: Accepted publickey for locadm from 192.168.15.20 port 55772 ssh2: ED25519 SHA256:xxxxxxx
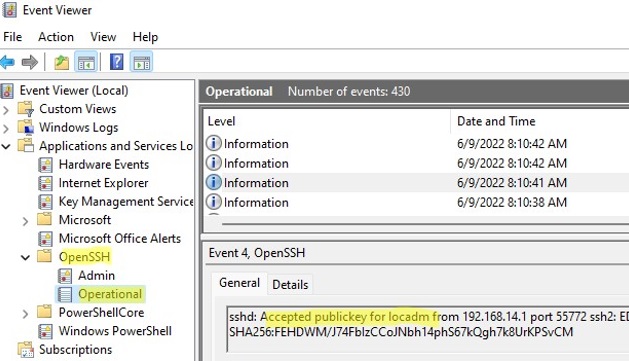
If you set PasswordAuthentication to no, and configure SSH key authentication incorrectly, then an error will appear when connecting via SSH:
user1@192.168.13.15: Permission denied (publickey,keyboard-interactive).

DenyGroups Administrators
So, you have configured SSH key-based authentication in Windows using a public/private key pair. This authentication method can be used to securely access remote servers, for SSH port forwarding (tunnelling) scenarios, to run scripts, and perform other automation tasks.
5 comments
Thank you – very complete guide.
Thank you soo much. it helped a lot.
I am trying to connect via ssh to a machine. and i get
permission denied public key
server log contains:
Failed to open file:C:/ProgramData/ssh/administrators_authorized_keys error:2
debug1: Could not open authorized keys ‘__PROGRAMDATA__/ssh/administrators_authorized_keys’: No such file or directory
Thanks for this, although I did try the administrators_authorized_keys route, but still failed, once commented out in the sshd_config worked a treat, thanks.
You can restrict accepted key types in %programdata%\ssh\sshd_config:
PubkeyAcceptedKeyTypes ssh-ed25519-cert-v01@openssh.com,ssh-rsa-cert-v01@openssh.com,ssh-ed25519,ssh-rsa,ssh-dss